Entra ID intranet SSO: turn Entra, Keycloak, or Google Workspace groups into roles
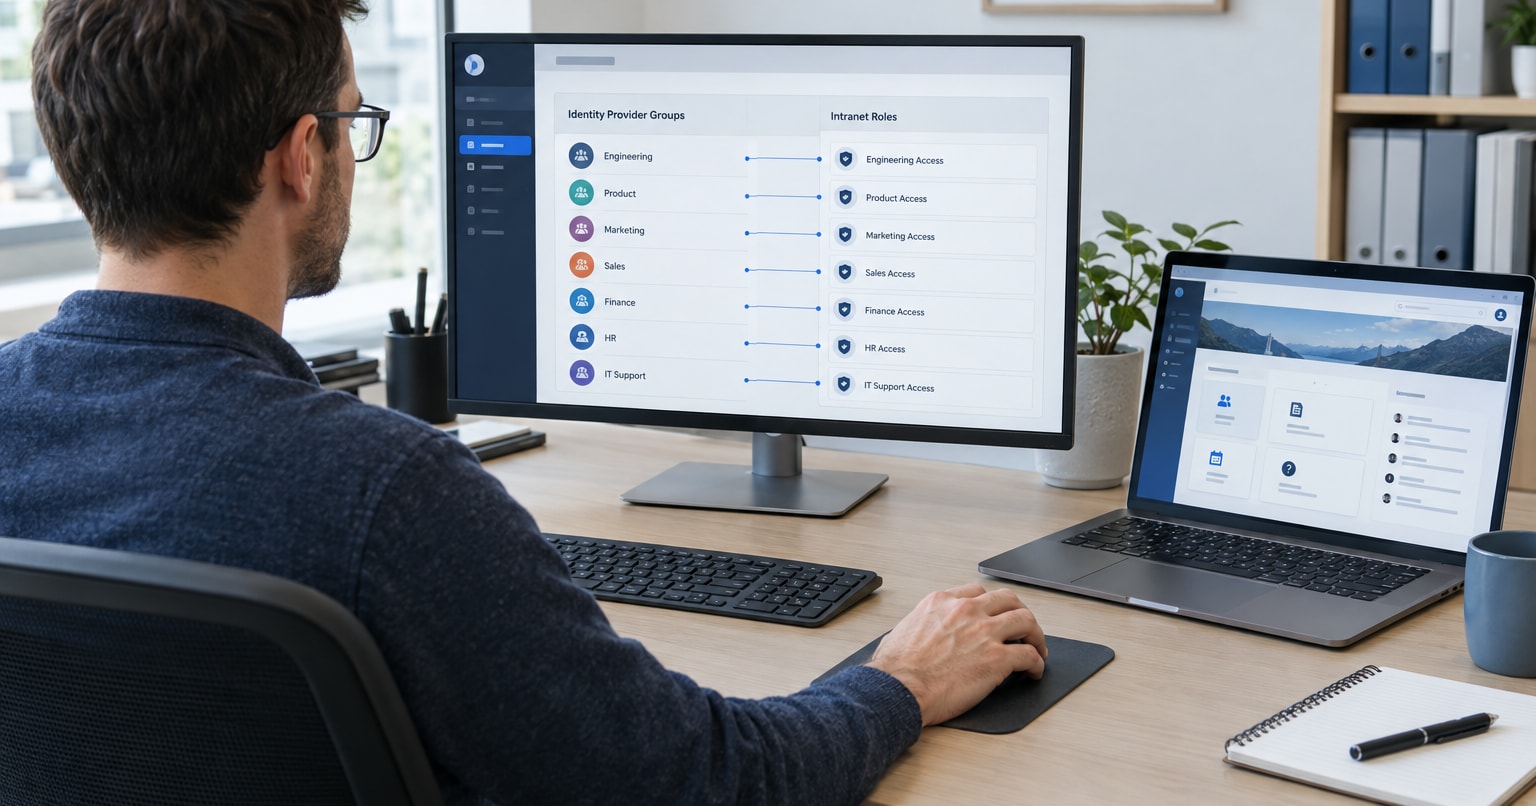
Can adding someone to an identity provider group give them the right intranet access? Yes, with a configured integration. Entra ID intranet SSO can let IT maintain access assignments in one place instead of repeating them in the intranet. The same principle applies to Keycloak and Google Workspace.
But group-based permissions, account creation, and account removal are separate parts of that setup. Open Intranet has a ready Keycloak integration recipe; Entra ID and Google Workspace need integration work. The goal is not just to let employees sign in, but to keep access correct when they change jobs or leave.
In this article:
- Can the groups we already use control intranet access?
- What do OIDC, SAML, and claims actually do?
- What is ready for Keycloak, and what needs integration work?
- How do we map provider groups to intranet roles and content groups?
- Can sign-in be limited to one security group?
- Does adding someone to a group create their account immediately?
- What happens when an employee leaves?
- Ready to start?
Can the groups we already use control intranet access?
Yes. A configured connection can use existing identity provider groups to decide who may enter the intranet and what they may do there. IT can then maintain those assignments in the provider instead of updating each employee twice.
However, creating a provider group does not automatically create an intranet role or connect it to permissions.
Consider a hypothetical setup:
- Intranet users allows employees to sign in.
- HR editors allows selected employees to edit designated HR content.
- Chicago location controls access to content restricted to that location.
These are separate decisions. Being allowed into the intranet should not automatically grant editing rights. Likewise, belonging to an editor group should not bypass the entry requirement.
The integration needs explicit rules connecting trusted provider information to intranet permissions. Those rules must cover both granting access and withdrawing it when membership changes.
For Open Intranet, Keycloak has a ready integration recipe. Entra ID and Google Workspace require integration work. A ready recipe provides a starting point, not a guarantee that every permission or account-lifecycle requirement is already covered.
What do OIDC, SAML, and claims actually do?
OpenID Connect, usually called OIDC, and SAML let the intranet trust authentication performed by an identity provider. Employees use their organization’s sign-in process rather than a separate intranet password.
Two concepts matter:
- Authentication: Who are you?
- Authorization: What may you access?
SSO establishes identity. Group and role mapping adds authorization rules.
With OIDC, identity information arrives through tokens, particularly the ID token. SAML uses assertions containing identity information and attributes. A claim or attribute is a named piece of information, such as an employee identifier, group membership, or application role.
Claims are inputs to permission rules. They are not permissions by themselves.
The access sequence looks like this:
- The employee authenticates with the identity provider.
- The intranet integration validates the provider’s response.
- An entry rule decides whether the employee may sign in.
- Mapping rules assign the appropriate intranet access.
Choosing OIDC or SAML does not establish that a suitable connector and all required mapping behavior are already available in Open Intranet.
Group information also may not appear in the default sign-in response. Depending on the provider, it requires claim configuration, protocol mappers, SAML attributes, or a separate directory lookup.
For background on the protocols, see the OpenID Connect overview and Microsoft’s SAML documentation.
What is ready for Keycloak, and what needs integration work?
The important distinction is between provider capabilities and what the intranet integration actually implements.
| Provider | Open Intranet starting point | Available group or role information | Work to plan |
|---|---|---|---|
| Keycloak | Ready integration recipe | Protocol mappers can supply group membership and role information | Configure the client and claims, establish mappings, and confirm account and access-update behavior |
| Entra ID | Integration work required | Configured group claims or application roles | Select and configure the connector, implement entry rules and mappings, and handle missing or over-limit group information |
| Google Workspace | Integration work required | Standard Google OIDC claims omit Google Groups membership; custom SAML apps support group membership attributes | Choose a suitable SAML integration or separate directory lookup, then implement and test access mappings |
Keycloak: a ready recipe with configuration still required
Keycloak’s protocol mappers can supply group membership and role information to applications.
Open Intranet’s ready Keycloak integration recipe is the starting point. The organization still needs its client connection settings, required claims, and access rules configured.
Before defining the project scope, confirm which mapping targets the selected connector supports and how it handles account creation, permission refresh, and removal. Do not assume that a ready sign-in recipe includes every lifecycle requirement.
Entra ID: plan authorization as well as sign-in
For Entra ID intranet SSO, successful authentication is only part of the work. The integration must also receive usable information for access decisions.
Entra can emit configured group claims. However, large group memberships can trigger an overage indicator instead of a complete group list. The integration must resolve that condition or use an appropriate application-role design. It must not treat an incomplete response as a complete membership list.
Microsoft documents both group claims configuration and application roles. The appropriate approach depends on the tenant, assignment model, and connector behavior.
Google Workspace: choose how membership reaches the intranet
Standard Google OIDC claims do not include Google Groups membership. Signing in with a Google account therefore does not automatically give the intranet enough information to apply group-based permissions.
Google Workspace supports group membership attributes for custom SAML applications. A separate Directory API lookup is another route to assess.
Neither route means Open Intranet already includes the necessary connector, lookup, or mapping behavior. Those capabilities need integration work and testing.
What counts as built-in, configuration, or custom work?
Open Intranet’s underlying Drupal platform provides roles and permissions. Connecting external identity information to those roles is a separate task.
The practical split is:
- Platform capability: Drupal roles and permissions.
- Ready recipe: The Keycloak integration starting point.
- Configuration: Provider settings, claims, and mappings supported by the chosen connector.
- Additional integration or custom work: Unsupported lookups, content-group assignments, synchronization, or account-lifecycle behavior.
Do not assume an optional connector or provisioning module is included by default. Confirm those components in the implementation scope.
How do we map provider groups to intranet roles and content groups?
Start with the access decisions the business needs, then configure the technical connection.
1. Write an access table
HR and internal communications should define who needs to read or edit which content. IT can then connect those requirements to provider groups.
The following example is illustrative. These are not Open Intranet default roles or group names.
| Source group | Intranet target | Intended access |
|---|---|---|
| Intranet users | Entry rule plus an employee role | Sign in and read general employee content |
| HR editors | HR editor role | Edit designated HR content without unrelated administrative permissions |
| Chicago location | Chicago content-group membership, if supported and configured | Access content restricted to that location |
| No Intranet users membership | Denied entry | No employee access through this sign-in route, even when another mapped group is present |
This table prevents a common mistake: treating permission to sign in as permission to edit.
2. Choose stable source identifiers
Use stable group identifiers where the provider and connector support them. A mapping tied only to a display name can break when a department or group is renamed.
Also decide whether direct membership, nested membership, or both should count. Providers and assignment mechanisms do not all handle nested groups the same way.
3. Make the required information available
Configure the provider to send the required claims or SAML attributes, or implement the agreed directory lookup.
Then connect that information to the access table. A claim appearing in the provider response does not prove the intranet has applied the intended permissions.
4. Separate allowed actions from content boundaries
An intranet role determines allowed actions, such as editing content. Content-group membership can determine where those actions apply when the relevant access controls are configured.
For example, an HR editor might be allowed to edit HR pages without being allowed to edit every department’s content.
Adding someone to a content group only protects content if access rules enforce that boundary. A department label or audience filter alone is not proof of restricted access.
5. Define refresh and removal behavior
Login-time mapping updates access when an employee signs in. It does not guarantee an immediate update after a provider-side membership change.
Agree on:
- When membership changes reach the intranet.
- Which permissions the integration owns.
- How it removes permissions that no longer have a source membership.
- Which separately governed local assignments must remain untouched.
Without removal rules, access can accumulate as employees move between teams.
6. Test allowed and denied actions
Test an ordinary employee, an editor, someone in several groups, and someone whose membership has been removed.
Check direct links to restricted content, not just whether a navigation item disappears. Confirm that losing an editor group removes editing rights and that losing the entry group prevents access through the intended route.
Supported mappings are configuration. Assignment or synchronization behavior the connector cannot perform needs additional integration or custom work.
Can sign-in be limited to one security group?
Yes, if the implementation explicitly enforces that rule.
An “Intranet users” group can control entry, while other groups determine permissions after entry. But group-to-role mapping alone is not an entry restriction. Without a separate check, an unmapped user might still receive default authenticated access.
There are two main places to enforce the restriction.
At the identity provider: In Entra ID, an enterprise application can require user assignment. Group-based application assignment has licensing requirements, and nested group membership does not cascade through that assignment mechanism. Check the tenant’s setup against Microsoft’s application assignment guidance.
At the intranet: The integration can check a trusted group or role claim, or an authorized directory lookup result, before admitting the employee.
For an entry rule based on membership, missing authorization information should deny entry. An unresolved group-overage response should not silently grant default access.
Test at least these cases:
- An employee who was never assigned access.
- An employee removed from the entry group.
- An authenticated employee whose response lacks the required membership information.
- A user trying a local or alternative login route.
Also test an employee with an existing intranet session. Denying the next sign-in does not automatically terminate an active session. Entry restrictions and session controls need separate acceptance tests.
Does adding someone to a group create their account immediately?
Not necessarily. The answer depends on whether the integration uses account creation at login or provisioning independent of login.
Account creation at first login
With just-in-time account creation, the integration creates a local account at the first successful authorized login, if the selected connector supports that behavior and it is enabled.
The sequence is:
- IT adds the employee to the required provider group.
- The employee signs in to the intranet.
- The integration validates identity and checks entry eligibility.
- It creates the local account and applies supported mappings.
Adding the employee to the provider group makes them eligible. It does not itself create their intranet account.
An agreed stable identity match is also important. Later sign-ins should update the same account rather than create duplicates after a name or email change.
Provisioning before the first login
Provisioning creates or updates local accounts independently of an employee’s login.
This matters when HR needs a new employee to appear in the directory before their first visit, or when access changes must reach the intranet without waiting for another login.
SCIM, directory synchronization, and scheduled imports are possible implementation routes to assess. They are not confirmed default Open Intranet features.
SCIM defines a standard for managing identity resources, but it still requires compatible endpoints and integration. A one-time import is only a snapshot. Ongoing provisioning needs matching, update, and deactivation rules.
The useful project question is: “Must the account exist before the employee signs in?” That answer helps determine whether login-time creation is enough.
What happens when an employee leaves?
Offboarding has three separate tasks:
- Prevent future provider authentication or application access.
- End or expire existing intranet sessions.
- Block or update the local intranet account.
Completing one does not prove the other two have happened.
Disabling the provider account can prevent future authentication, but the intranet may still have its own active session. Microsoft’s access-revocation guidance distinguishes provider-controlled sessions and tokens from application-controlled sessions.
That means session termination, supported logout behavior, and expiration limits need an agreed implementation.
Login-time mapping is not enough for leavers
An employee who never signs in again will not trigger another login-time update. Their local account and old role assignments may remain unchanged.
Event-driven or scheduled lifecycle synchronization can address this, but it is additional integration work unless explicitly included in the agreed setup.
The required timing should be clear. “Access ends at the next login” and “access ends at session timeout” are not the same as immediate revocation.
Blocking and deleting are different decisions
Blocking an account can prevent its use while preserving content ownership and history.
Deleting an account requires a separate decision about retained records, attribution, and organizational retention requirements. HR, IT, and the relevant records or compliance owner should agree on that policy before automating deletion.
Test the complete offboarding path
An acceptance test should:
- Remove the employee from the access group.
- Disable the provider account.
- Attempt a fresh sign-in.
- Revisit restricted content through an already active session.
- Inspect the local account’s status and permissions.
- Record how long each change takes to become effective.
This gives the organization evidence of what “access removed” actually means.
Ready to start?
Your existing identity groups can reduce repeated access administration, provided the integration covers entry, permissions, account creation, and removal.
Keycloak has a ready Open Intranet integration recipe. Entra ID and Google Workspace need integration work. For every provider, the configuration and any custom work should be agreed against specific access and offboarding tests.
Talk to the Open Intranet team with three details:
- Your identity provider.
- One example group-to-permission mapping.
- Whether employees must appear in the directory before their first login.
Include your required access-removal timing. Together, we can separate the ready starting point and configuration tasks from the integration work needed to keep employee access correct.